February 24 - 28, 2020 | Moscone Center | 747 Howard Street | San Francisco, California 94103 | Learn More
Our RSA Conference 2020 coverage was made possible by the generosity of our sponsors.
We are ever so grateful for your support!
RSA Conference USA 2020
Yes, of course, we had another road trip full of incredible events, podcasts, webcasts, and all sorts of conversations—all At The Intersection Of Technology, Cybersecurity, and Society.
Traditional Daily Recaps from all over the place throughout the Moscone Center.
Everyday, we invited a select handful of people to join us to talk about what happened, what is happening, and what isn’t. As you have seen from previous years, we aim to have some fun as we update you directly from the #RSAC2020 floor. Our guests didn’t disappoint us this year. Watch or listen—the choice is yours!
Day Four with Malia Mason, Jessica Bair, and Neil “Grifter” Wyler
Prefer a podcast? Have a listen.
Day Three with Thom Langford, Andrea Frost, Javvad Malik, and Chris Pierson
Prefer a podcast? Have a listen.
Day Two with Steve Schlarman, Allison Ockerbloom, and MK Palmore
Prefer a podcast? Have a listen.
Day One with Alyssa Miller, Mark Albertson, and Caroline Wong
Prefer a podcast? Have a listen.
Be Sure To Listen to our Pre-event Podcasts: Our Famous Chats On The Road To RSAC San Francisco 2020.
Podcasts recorded with organizers, keynotes, and speakers to prepare you for what will be coming.
#1 What to expect during RSA Conference San Francisco 2020?
A conversation with Linda Gray Martin (Sr. Director & General Manager, RSA Conference) and Britta Glade (Director, Content and Curation at RSA Conference)
PUBLISHED
#2 Presenting the Ally of the Year Awards 2020 Celebration.
A conversation with Carmen Marsh (Organizer) and Jessica Robinson (Committee Member)
PUBLISHED
#3 The Impact of the Human Element on Geopolitics and CyberSecurity.
A conversation with Juliette Kayyem. Professor, Harvard’s Kennedy School of Government
PUBLISHED
Catch us on video with a variety of guests in the RSAC Broadcast Alley and in the RSA Conference SOC.
At The Edge | What Happened In The SOC At RSA Conference 2020
with Jessica Bair And Neil Wyler
PUBLISHED
At the Edge | A CISO Panel with Sean Martin
with Deborah Blyth, Nils Puhlman, and Laz
PUBLISHED
The Cyber Society | What Makes A City Smart? The Technology Or The People?
with Remi Cohen and Lan Jenson
PUBLISHED
The Future of the Future | When Humans and Robots Co-Exist
with Sara Boddy and Jason Elrod
PUBLISHED
The Academy | Hackers Rights: When Breaking the (current) Law Doesn’t Mean Breaking the Rules
with Chloé Messdaghi, Jeff Boothby, and Tanner Emek
PUBLISHED
The Academy | State Of Cyber Education Awareness
with Angel Grant and Andrew Woodward
PUBLISHED
The Academy | Diversity's Impact On Business And Security Strategies
with Angel Grant and Chloé Messdaghi
PUBLISHED
Many Their Stories Podcasts with our sponsors.
These will be recorded before, during, and after the event—many have been published and can be found below on this page. You can also find these and all of the other Their Story segments we’ve recorded here. If you want to tell your story with us AND attach your brand to our RSAC Coverage activities, you can learn more here.
Ally of the Year Awards 2020 Celebration
AYA 2020 Celebration in San Francisco on February 23, 2020
We came together to celebrate allies who work to advance equality and make a substantive difference for women in technology.
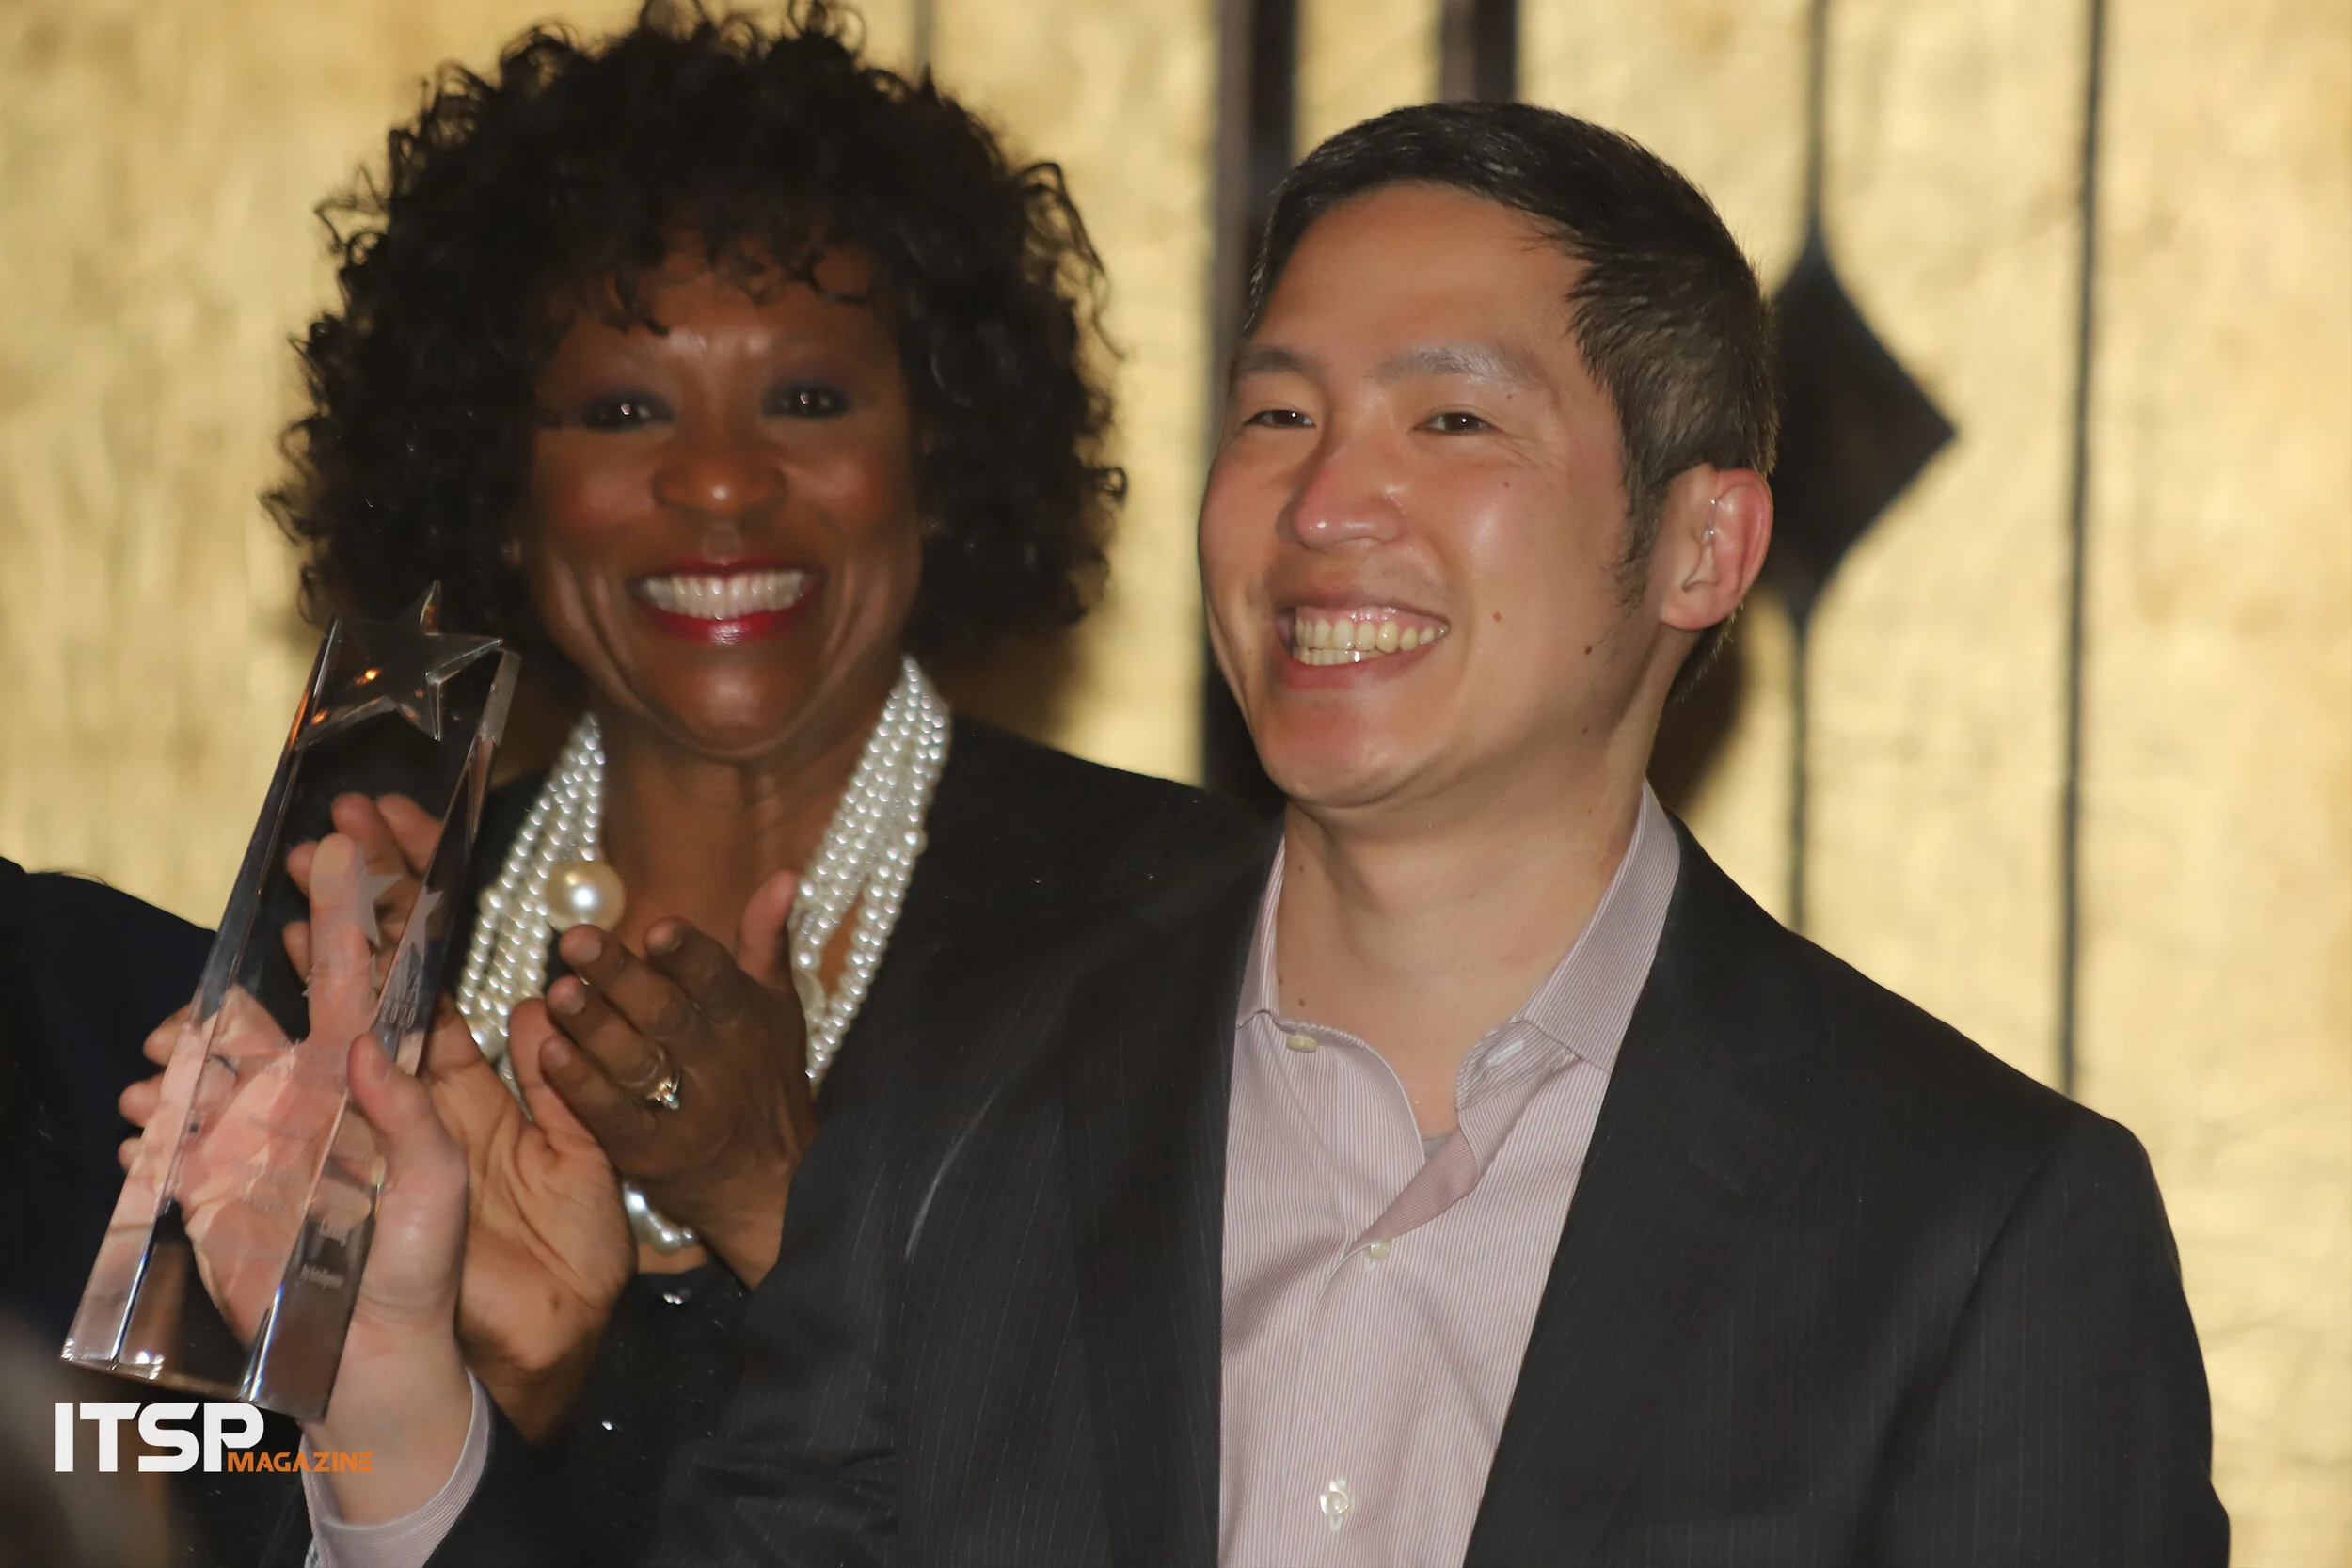
ITSPmagazine was nominated as one of the three finalists for the media award and we couldn’t possibly be more proud. Thank you for all who voted for us — and a big applause to all the other finalists in all categories. We are very grateful to also announce that we were selected as the winner of the Media Ally category. Thanks to everyone that supports our efforts to promote a diverse and inclusive InfoSec community and Cyber Society!
P.S. *A Chats on the Road podcast is here!
Winners of the 2020 AYA Awards: InfoSec Girls, Nathan Chung, ITSPmagazine, Cybrary, McAfee, Kathleen Smith, WiCyS, Adam Benson
Expert Conversations Filmed In The RSA Conference Broadcast Alley and the RSA Conference SOC
Hosts: Sean Martin & Marco Ciappelli
Guests: Remi Cohen And Lan Jenson
If you are old enough or enjoy "vintage" cartoons, you may be familiar with The Jetsons—a 1960s/1980s TV show about a family living in a futuristic place called Orbit City. The architecture is Googie style, technology is absolutely everywhere, and all homes and businesses are high up in the sky supported by very tall columns. No need, in this conversation, to dig into the possible environmental or societal catastrophe that may have forced this solution. And, let's keep it as a joke about how that, in the year 2020, there is no such city; and why we are not living that life?
There isn’t a single answer, as this is—just like with every other technological topic—both a global conversation that has the common thread of development and well-being of humanity…and a local conversation with as many different angles that are defined by the cultural diversities, various needs, and short/medium-term goals we may find in different parts of the globe.
In this session, we spoke about surveillance, privacy, safety, IoT, resilient ecosystems, education, and the roles of individuals, communities, nonprofit groups, governments, businesses, and all decision-makers that must come together to drive this change. All of this in the interest of those that will ultimately either be damaged or could benefit from the present and future smart city transformation: the citizens.
Hosts: Sean Martin & Marco Ciappelli
Guests: Angel Grant And Chloé Messdaghi
Does your business and security strategy include diversity and inclusion? No? It might be time to go back to the drawing board.
If you are reading this, I am assuming you are human. As a human being, I am also going to think that we share many traits—both physical and behavioral. I am also going to assume that we are very, very different people.
One thing that we tend to forget is that what makes humanity so special is the incredible diversity of which it is made.
In this conversation, we are going to focus on the value of diversity for our industry—cybersecurity—and we will leave the anthropological, sociological, and philosophical discussions for another time, and another place.
Chloé Messdaghi and Angel Grant joined us during RSA Conference to discuss the value of diversity and inclusion as a means to build strong teams, products, and solutions—and to attempt to understand why, at the same time, it represents such a big problem for so many.
If you are interested in understanding why diversity and inclusion are one of the most significant values for your company and your team, how you can make it part of your hiring process, how to leverage it in your day-to-day operations, then this is going to be a conversation worth your time. If you're not interested, you may not get the results otherwise possible.
Either way, stay open-minded and enjoy it.
Hosts: Sean Martin & Marco Ciappelli
Guests: Angel Grant And Andrew Woodward
In this conversation, we discuss the role of education in building the next generation of the workforce for the cybersecurity field and how companies and universities can work together to achieve the same goal. Ultimately with better results.
“Companies are made of people” is an old saying that too often we tend to forget, just as we forget that people also build the technology and are ultimately responsible for the future of this and the CyberSecurity industry. As the Digital Revolution keeps moving forward at an oft-restless pace, the roles are becoming more interconnected and so new careers, new educational programs, and new work backgrounds must include skills not even considered relevant a few years ago.
The talent gap is real but is not just an industry gap; it is also an educational institution gap that can be filled with being creative, open-minded, practical, diversity-oriented programs; educating new generations with a mindset of lifelong learning attitude will also prove valuable.
We discuss this and much more, with our guests. And, as it often happens at ITSPmagazine, this conversation starts and ends with the human element. If you are human, we invite you to listen up, and enjoy!
Hosts: Sean Martin & Marco Ciappelli
Guests: Sara Boddy and Jason Elrod
Fortunately, for this chat, we have a wide range of experience and wisdom from our guests—Sara Boddy and Jason Elrod—as we can look at the capabilities and risks these technologies bring to the table, coupled with how we will need to adapt to a world where we will share tasks—and associated responsibilities—with things that are not human.
Where do we end up in 5 years? Ten years? Beyond that?
This is not about a robot that can clean the floor; this is about moving towards a society where robotics and AI will enable us to extend our humanity beyond the limits of our current human capabilities. A full-scale deployment is not to close, but robotics and AI are among us as we type, and the big revolution may happen sooner than we are ready.
This is why we need these conversations—many of them.
Intrigued? Yeah, me too—and I was there.
Enjoy.
Hosts: Sean Martin & Marco Ciappelli
Guests: Jessica Bair and Neil Wyler
During this exclusive behind-the-scenes interview, Sean and Marco chat with Jessica Bair from Cisco and Neil Wyler (aka Grifter) from RSA Security about the connection between the human element and the technology—along with the collaboration between teams, technology, and intelligence.
Hosts: Sean Martin & Marco Ciappelli
Guests: Chloé Messdaghi, Tanner Emek, and Jeff Boothby
In today's conversation, we are joined by Chloé Messdaghi, Tanner Emek, and Jeff Boothby as we take a direct view into the role and the impact that current laws and a lack of understanding outside of the InfoSec industry can have—and does have—on the ethical hackers' lives… and, ultimately, in our society.
We must recognize that ethical hackers aren't cybercriminals—the work that they do matters. As we look for ways to protect our homes, our cars, the stores where we shop—and we want to have a safe Internet as well—we must come to terms with the reality that hackers are part of the solution, not part of the problem.
Not convinced? Have a listen and decide for yourself.
Hosts: Sean Martin & Marco Ciappelli
Guests: Laz, Deborah Blyth, and Nils Puhlmann
This is a conversation I’ve been dreaming about having for quite a while myself. My dream finally came true as Laz, Deborah Blyth, and Nils Puhlmann—current and former CISOs—joined us to look at the role, their teams, their processes, their technologies, the culture, and so much more.
CISOs are humans too—and they dream just like the rest of us. The question is: what do they dream about? Let’s find out.
Chats on the Road to San Francisco 2020
As part of our RSA Conference USA 2020 coverage, we hit the road—Marco and Sean made their way to San Francisco to connect with a number of the RSAC organizers, keynote speakers, presenters, panelists, and more. This time by plane.
During these conversations, we got a sneak peek into what they planned to share at the conference as well as a glimpse into their backgrounds and some additional insight on the topics they are passionate about as cybersecurity, privacy, and compliance professionals.
These are the chats — enjoy!
By Sean Martin & Marco Ciappelli
As the former Secretary at the Department of Homeland Security, our guest today, Juliette Kayyem, has probably seen some things that most people and organizations would have serious nightmares about. And, to open up our conversation, she tells that she thinks about really scary stuff all the time and now tries to help others identify and reduce the risk of the bad things happening.
If you listen carefully, you will realize that your InfoSec journey doesn’t have to feel like an old, run-down rollercoaster. Listen to this podcast with Juliette to get some insights on what it takes to protect ourselves, our businesses, and our society, as she prepares to take the keynote stage at RSA Conference 2020 with Admiral James Stavridis.
By Sean Martin & Marco Ciappelli
The AYA 2020 Celebration in San Francisco takes place on Sunday, February 23, 2020. Please join us in celebrating allies who work to advance equality and make a substantive difference for women in technology.
To kick our celebratory coverage off for this event, we have the pleasure of chatting with the event’s leader, Carmen Marsh, along with one AYA committee member and judge, Jessica Robinson.
We are honored to be part of and to support this event as it shows that it is the numbers that make us stronger—all of us working together can bring the positive change we need.
Ultimately, as Jessica points out, it’s about making an impact—taking this from conversation to action—taking this from action to positive impact. We can get there. Join us!
By Sean Martin & Marco Ciappelli
The theme for this year’s RSA Conference, which our podcast guests are going to tell us all about, is one that's right up our alley here on ITSPmagazine—The Human Element. And, there's a lot going on during the week of RSAC, all designed to help educate and connect the InfoSec professional and community as they look to arm themselves to be successful in their roles and happy and healthy in their InfoSec lives.
During our chat, in addition to hearing about the decision to select the human element as this year’s theme, we also get additional insights from them regarding what the conference attendees should expect, including:
- Some keynote session picks
- Some Learning Lab picks
- What the Engagement Zone is all about
- College Day and other programs for students of nearly all ages
So, what are you waiting for? Have a listen to Linda and Britta to learn more—then join us and the rest of the community in San Francisco.
Additional RSA Conference San Francisco 2020 Coverage Support by:
RSA Conference 2020 Photo Gallery
Are you feeling nostalgic? This is the recap of what happened last year…
Their Story Podcasts From RSA Conference 2020
We love helping people and companies tell their stories. Of course, we don’t have unlimited bandwidth to do this all the time for all of the companies out there — so we must be selective. These are the stories that these companies really wanted to share with our audience. We hope you enjoy them!
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Josh Bohls
A picture is worth a thousand words. Why is that? Because humans like to visualize things.
While written words and checkboxes help us manage our tasks, often, it’s a picture—or a diagram—or a scanned document—that can make all the difference in the world.
The potential business workflows, scenarios, and use cases are endless. Examining them will uncover the question, are we taking advantage of new mobile-ready capabilities? Or, are our existing business processes keeping employees chained to the office? And, especially in the new age of pretty much everyone working from home, it begs an even bigger question: how are the in-office workflows working out?
These questions, and many more, are discussed during this chat with Josh Bohls, founder and CEO of Inkscreen. If you have business processes and are looking to make the most of text and images to keep your business workflows running smoothly—AND SECURELY—you’ll want to listen to the Inkscreen story.
Ready? Then have at it!
A Their Story conversation with Sean Martin and Marco Ciappelli
Guests: Guy Givoni and Paul McCarty
We were fortunate to meet Guy Givoni and Paul McCarty during their RSA Conference Launch Pad event in Singapore. They’ve been busy riding the wave of success following that event and we caught up with them in San Francisco during RSA Conference 2020 to get an update from them.
Are you ready to learn more? Good! Have a listen to their story.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Corin Imai
Having met Corin Imai in many roles and many locations over the years, we were thrilled to finally sit down with her and hear her story - which includes the work she is doing at DomainTools. There’s a lot to what Corin and the team of data scientists are up to. Have a listen as she shares some of their work with us during this chat.
It is a good story. Enjoy.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Benny Czarny
Before we get to the start of this story, our journey here begins with a view of the current moment in time: OPSWAT’s focus on protecting our critical infrastructure.
You might be surprised (or, maybe not) that several organizations that the OPSWAT team has connected with don’t have a decent answer to this question, with many lacking any policy to define what is appropriate vs. what shouldn’t be allowed. Something as simple as the introduction of a malicious Excel spreadsheet that bypasses the antivirus sandbox capabilities can create a situation where a power plant can be taken offline.
So, What does the future hold for securing our critical infrastructure? Listen to Benny Czarny, CEO, and founder of OPSWAT, as he enlightens us during this chat.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Dana Tamir
During RSA Conference 2020, we had a chance to connect with Dana Tamir from Silverfort to get the updated Silverfort story. During our chat, Dana points out that enabling secure authentication and zero trust policies without requiring an agent or proxies or software changes should be the primary goal for organizations looking to keep bad actors out while ensuring secure access to those that have been granted authorized access to the business resources.
Dana provides several use cases and workflows to help demonstrate the scenarios discussed during our chat. How many of these scenarios does your organization deal with? Have a listen to learn more.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Mounir Hahad
During RSA Conference 2020, Juniper Networks announced its ability to analyze encrypted traffic, bringing visibility and context to the network where threats and attacks continue to move toward a world of darkness. From the release: It permits organizations greater visibility and policy control over encrypted traffic, without requiring resource-intensive SSL Decryption.
We were able to speak with Mounir Hahad, Head of Juniper Threat Labs at Juniper Networks, to learn more about these new capabilities and the impact it can have on an information security program as organizations try to maintain visibility and control over their networks, systems, and data.
Have a listen as Mounir shares his thoughts on today’s state of cybersecurity, comparing it to the era of industrialization.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guests: Eoin Keary and Rahim Jina
For five years running, Edgescan has conducted an annual survey to analyze the state of vulnerability assessment programs within organizations across the globe. With new data points in hand, giving their team the ability to evaluate year-over-year changes, this year’s results raise the obvious question: “Have we learned anything to help make our businesses more secure?”
Some technologies aren’t the silver bullet, and the human element is still critical as they bring the risk assessment to the table. With this point in mind, assuming you are human, you may want to listen to this chat and also read their report to get a view into how you can work with your peers—and the technology—to reduce risk through full-stack vulnerability management.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Rohit Ghai, CEO, RSA Security
The InfoSec industry has done a lot of work to raise awareness around the risks we face in business and society, thereby increasing the appreciation for the need to protect our companies and ourselves from cybercrime, fraud, and other dangerous activity associated with being connected to the Internet. Unfortunately, the stories that have been told—and the stories that the media pick up and amplify—are often those that paint a picture of doom, and gloom, and failure.
Ultimately, it may be that we aren't defining the ending to our stories in a way that we want them to end. To this end, do we know what does it mean to win? For which side? Do we know what it means to lose? For which side? And, most importantly, does winning on one side equal losing on the other? In both directions?
Answering these questions can help us change the way we want our stories to be heard; it can help us improve the way we tell our story — can help us change the way we live our story.
Are you ready to change the narrative for a better story, a better outcome? Have a listen to this story, and then start telling yours.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guests: Alison Furneaux and Padraic O’Reilly
The concept of governance, risk, and compliance (GRC) has been around since the mid-2000s. GRC continues to change, as do business models, the technologies that run the business, and the cyber threats that threaten to bring it to a screeching halt.
Of course, the role of the CISO has also changed, but has it kept up with the times?
Listen to the CyberSaint story to hear how they identified this problem and have been working diligently to help CISOs overcome the challenges they face.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Colin Bastable
Organizations are defined by their culture—and the culture is determined by the collection of individuals that make up the organization. Organizations that take information security seriously and work with their employees to understand and embrace their role in protecting themselves and the business are the organizations that stand a better chance of thwarting off an attack.
According to today’s guest, Colin Bastable, 97% of all of the threats originate with some form of social engineering. So, organizations must work on having an understanding of the human angle as it relates to these threats—both the employees as humans and the cybercriminals as humans. Organizations must understand the human motivation—both to attack and to protect themselves. People are people on all sides of the equation—it’s just how it is; it’s just how they are.
Once you have this understanding, coupled with how the protection technologies work, you can begin to identify the gaps between what the technology can offer and what the humans can do for themselves. It’s this gap that needs to be closed.
Are you interested in understanding how to identify and close this gap? Have a listen to this chat with Colin—he’s seen this in action all around the world in many different industries.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Michael Rezek
For years, organizations have been monitoring network traffic to squeeze every ounce of performance out of their systems and applications. The data collected and analyzed gives organizations tremendous insights into what changes need to be made to keep things up and running at top speed. This data is gold.
Many organizations stop mining and analyzing their data once they see that there’s gold there—effectively letting the platinum in their data to wash downstream. The platinum—at least in this story anyway—is security data.
Fortunately, Michael Rezek knows a bit about network data analysis, network performance, and network security—and recognizes the value of both the gold and the platinum sitting in the network data they monitor.
Have a listen to Michael as he shares the Accedian story, describing the journey they’ve taken as a company—and the journey they are helping others take as they continue down the path of their digital transformation.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Jason Kent
Since we are humans, we seem to be repeating all of these same mistakes in a different part of the application world—the API layer. We're forgetting that the API layer is really meant for computer to computer communications, changing the game for how we approach authentication, access control, communications, instructions, behaviors, and more. As one example, things like rate limiting can really become a problem if not addressed.
To help us understand this world better, have a listen to Jason Kent, Hacker in Residence at Cequence Security, as he shares with us some of the fun ways he hacks on applications—namely through APIs.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Christopher Pierson
Sometimes it takes some creative thinking when it comes to gaining an understanding of how information security and cybersecurity work—and why they matter, not only during work hours but after hours as well.
To help you with this thinking process, have a listen to this chat with Chris Pierson, founder, and CEO of BlackCloak, as he tells us (you) his story about the creation of BlackCloak and its cyber protection services for executives and high net worth individuals.
Who knows, you might even get a glimpse into what a BlackCloak is.
Enjoy!
A Their Story conversation with Sean Martin and Marco Ciappelli
Guest: Venu Rao
The team at WeSecureApp have been embracing that recognition, the positive feedback they receive from their clients, and the constructive feedback from the RSA Conference Launch Pad judges (in Singapore) to continue to expand their team, their presence around the world, and their product line — all with a focus on meeting customer need and market fit.
With an expansion into the US (with a Dallas, Texas office) and a key member added to their advisory board, WeSecureApp has found themselves benefiting from several accelerator programs that are setting them up for long-term growth and success.
Listen in as Venu tells us more about these activities and what the future holds for WeSecureApp.
A Their Story conversation with Sean Martin and Marco Ciappelli
Guests: Mario Vuksan, CEO & Co-Founder, ReversingLabs | Tyson Whitten, VP, Global Marketing, ReversingLabs
CHAPTER 2: Does the black box of machine learning and artificial intelligence give you a headache? If so, it’s like the lack of visibility into how new (dare we say, “next-gen”) information technologies work. This is beginning to give pause to many organizations looking to leverage such technologies to help them succeed with their IT security management programs. Without a view into how the data is analyzed paired with a lack of visibility for how the results can be connected back to the operations—and the business—means that organizations are forced to blindly trust that their vendors are doing the best things, the right thing.
So, how come we can’t get this visibility? What’s holding us back? Have a listen to Mario’s and Tyson’s view to hear how they see these headaches being treated in the not-so-distant future.
If you have a story of your own to share, we can help you to make that happen.
RSAC 2020 San Francisco Conference News and Coverage by ITSPmagazine
Live Panels • News • Articles • Blogs • Stories • Webinars • Webcasts • Interviews • Talk Shows • Videos • Recaps
Thank you for visiting ITSPmagazine's RSA Conference 2020 Event Coverage